





Uptime and host health
Uptime and host health monitoring on every customer deployment
Nettle raises $4.8M to scale the AI Workspace for Loss Control globally.
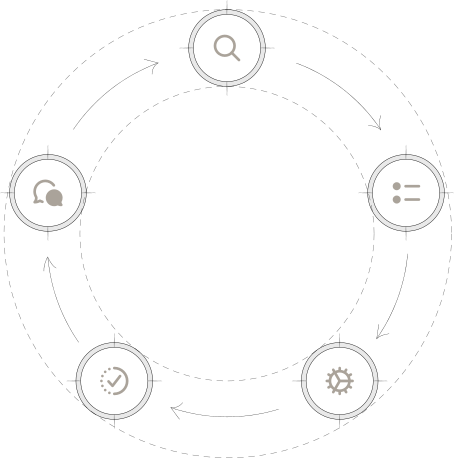
Read Announcement →Every night, we scan our code, dependencies and cloud for new threats. Critical fixes are raised the same night.
Automated threat sweep
Critical advisories triaged and fixed
Certified security management
Web, API and cloud tested annually
Checks vendor alerts, vulnerability databases and CISA’s list of actively exploited flaws.
Checks advisories against exact versions in our code, containers and customer cloud images.
Looks for access control gaps, injection and unsafe network calls before release.
Combines code, cloud and compliance findings so nothing goes unowned.
Logs evidence, severity, deadlines and draft fixes; verifies rollout everywhere next night.
Uptime and host health monitoring on every customer deployment
Attack and authentication alerts (brute force, credential stuffing, unusual access)
Malware scanning of every uploaded file, with the alert path tested end to end
Rate limiting at the edge and per client, so abusive traffic is throttled automatically
Application error tracking and background job alerting
Every release recorded, with confirmation that each customer is running it
AI features are held to the same bar as the rest of the platform, and tested for the ways AI systems fail
Model input & output guardrails required by and built with a global insurer’s security team
AI agents can only reach public web hosts, never your internal network
Dedicated AI red team test by an independent firm
Working towards ISO/IEC 42001 (AI management), with a gap assessment underway and a written Responsible AI policy
Choose OpenAI, Anthropic or Google to suit your team’s needs. All are contractually barred from training on your data.
Independent audits, regular testing and clear documentation for your team to review.
Request documentationCertified information security management practices.
Personal data protection in line with GDPR requirements.
Internal penetration tests conducted every quarter to assess security.
Annual external penetration testing across our web, API and cloud.
Dedicated testing by an independent firm to assess how our AI systems fail.
Recovery testing with measured recovery time and recovery point.
Incident response exercises covering the GDPR 72 hour notification path.
Our SOC 2 Type I audit is underway as part of our assurance programme.
A gap assessment is underway as we work towards ISO/IEC 42001.
No. Your data is strictly isolated and is never used to train, retrain, or fine-tune public or shared AI models. All inspection evidence, property records, and underwriting guidelines remain exclusively yours.
Critical issues are triaged the night they are published and fixed within our defined remediation SLA. We track every finding to the day it goes live on your deployment.
Yes. Each customer runs on a dedicated deployment with its own infrastructure, database and signing keys. On premises is also available.
Quarterly internal tests, plus an annual external test and an AI red team test by an independent firm. Summaries are available under NDA.
Enterprise SSO with Entra ID, SAML and OIDC is on our roadmap and can be delivered as part of onboarding.
In your chosen region, on dedicated infrastructure or your own premises. Model processing uses providers under no training agreements, with EU routing rolling out.
Retention periods are set per customer. On request or at contract end, data is deleted from your deployment and backups on a documented schedule.
Yes. Our Trust Centre at trust.getnettle.com has policies, certificates and pen test summaries, and our security team will join your review call.